
Offensive security since 2017 · Europe and worldwide
Penetration Testing, Red Teaming & AI Red Teaming
Senior, certified testers find what an attacker would, before an attacker does. Your report is ready within 48 hours of testing ending, in your own client portal.
- ISO/IEC 27001 & ISO 9001 certified
- Testers with CREST, OSCP+, PNPT and more
- DORA TLPT & TIBER-EU
Some of the certifications our testers hold

Our company is certified


Services
What we test
Senior testers lead every engagement, with our own AI taking on the repetitive work. Testing follows the frameworks and regulations that apply to you.
Threat-Led Penetration Testing
Intelligence-led red teaming for DORA TLPT, TIBER-EU and national TIBER programmes.
Learn more →Red Team Engagements
Realistic attack simulations that test how well you detect, respond and recover.
Learn more →AI/ML Red Teaming
Test LLM apps, AI agents and models against prompt injection, data leakage, jailbreaks and abuse.
Learn more →Application Penetration Testing
Web, mobile, APIs and thick clients, tested in depth by senior testers.
Learn more →Internal & External Infrastructure Testing
Find the weaknesses in your internal and external networks before attackers do.
Learn more →Cloud Security Assessments
From misconfigurations to lateral movement paths in your cloud deployments.
Learn more →Also: social engineering, adversary simulation, and hardware and IoT testing.
From first request to signed-off retest
How we work with you
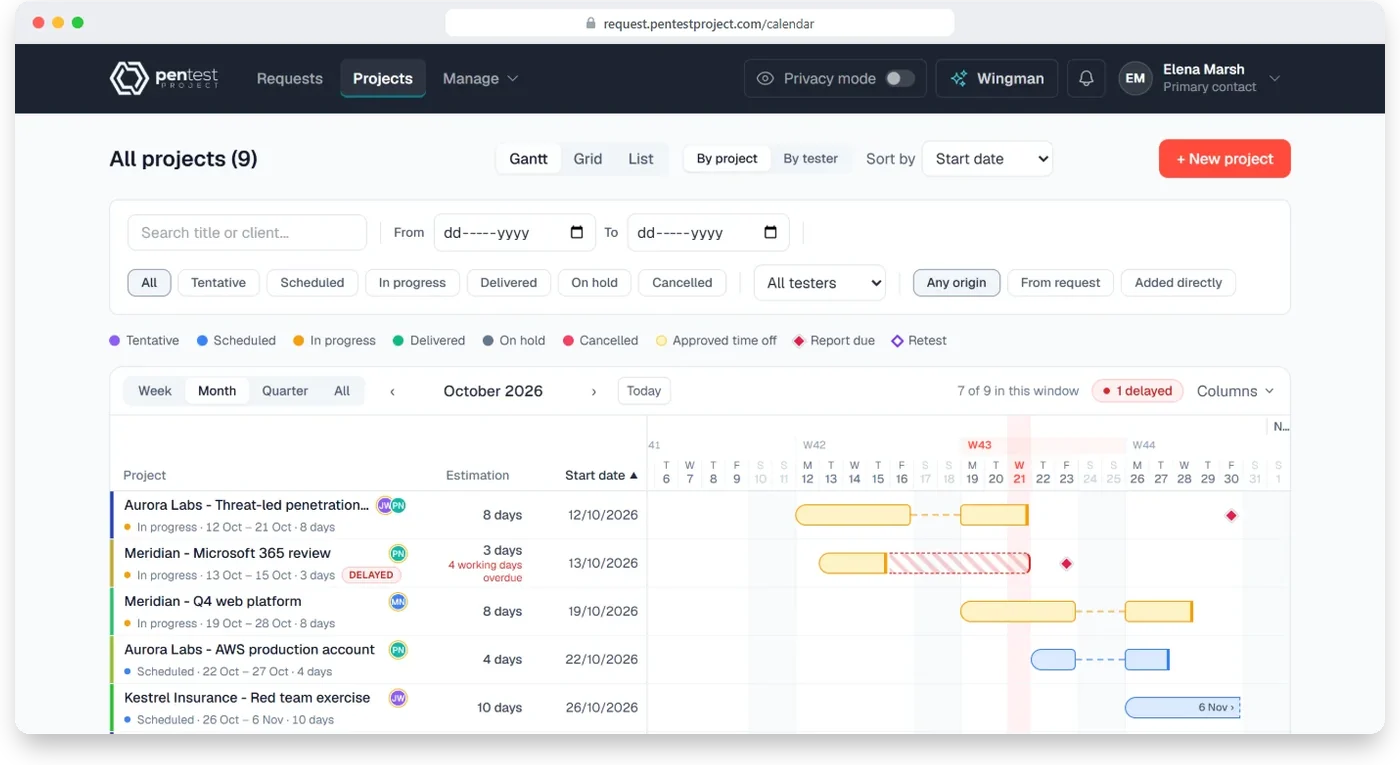
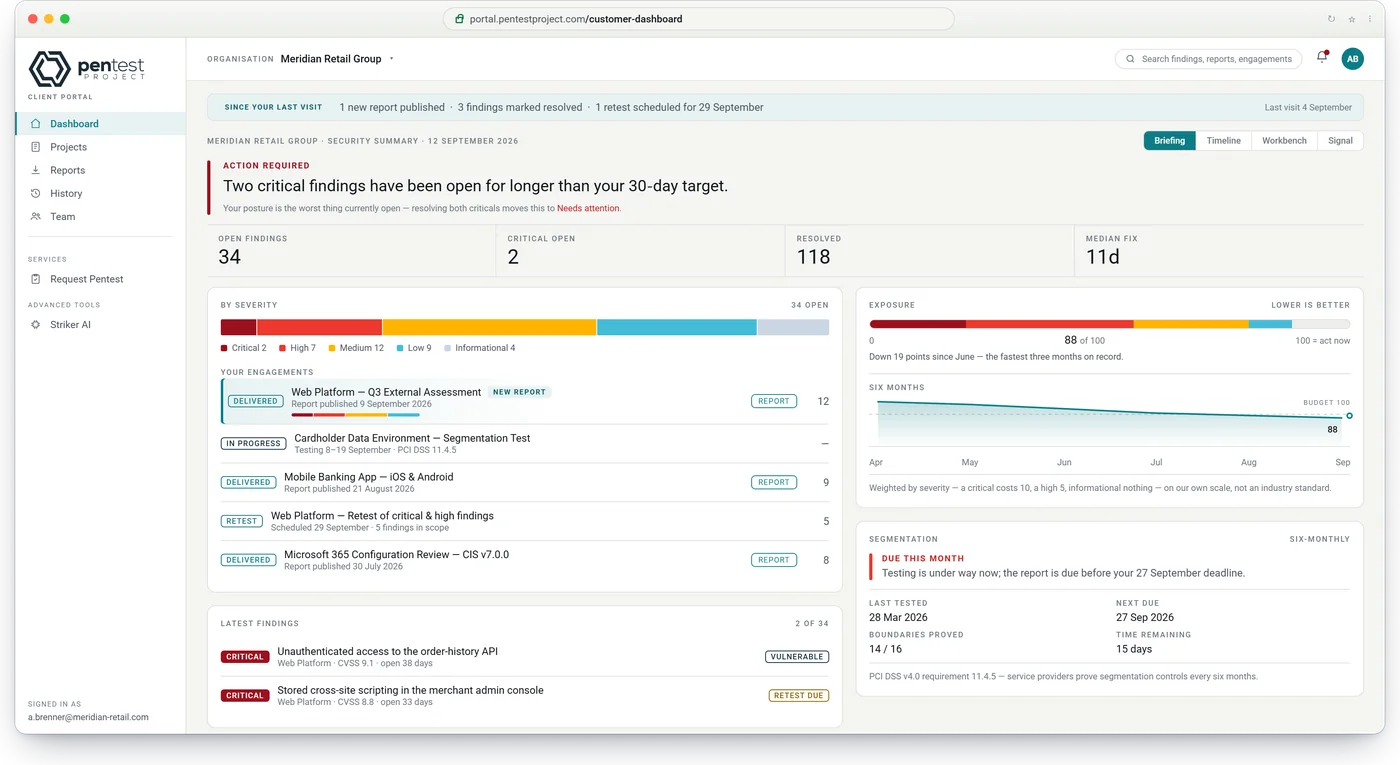
We built our own platforms so working with us is simple and transparent. Flint takes you from your first request to a signed statement of work. Slate, our client portal, holds your findings and reports.
Built by us, used by you. Flint and Slate are built by PenTest Project, our software arm (pentestproject.com). In Slate, you and your colleagues sign in with Microsoft Entra ID, Google Workspace or any OpenID Connect provider, or with two-step sign-in. Your administrator decides who sees which project.
Scope online Flint
Answer only the questions that apply to the services you need, and hand sections to colleagues with a link.
A precise proposal, signed online Flint
Effort, price and the statement of work are built from your answers. You review the proposal and sign it online.
Ready for day one Flint
A checklist covers authorisation, test accounts and change freezes. The technical kick-off ends with agreed rules of engagement.
Senior-led, AI-accelerated testing
Certified consultants lead every test, with manual testing wherever judgement matters. Striker AI, our own testing framework, takes on the repetitive work, always within the scope in your statement of work.
Your results in Slate Slate
Within 48 hours of testing ending, your report is ready in Slate. Review each finding with its evidence, follow your exposure over time, and download reports as PDF or Excel.
Remediate and retest Slate
Accept a risk or request a retest, finding by finding. Every issued report is kept, versioned, as evidence for your auditors. Retests are agreed per contract.
Why us
Why companies choose us
150+
penetration tests a year
100%
of engagements led by a senior tester
48h
from the end of testing to your report
2017
testing since, across Europe and worldwide
Senior people, every time
No juniors learning on your systems. Their certifications include CREST, OSCP+, PNPT, CARTE, AIRTP+ and more.
Human judgement, AI speed
Scanners and AI agents find the obvious at scale. Our testers chain weaknesses the way a real attacker would, guided by MITRE ATT&CK and current threat intelligence.
Reports your board and engineers can use
Every finding is ranked by business risk, with evidence and remediation steps your team can act on straight away.
Aligned with the OWASP testing guides (WSTG, MASTG, ASVS) and Top 10 lists, MITRE ATT&CK and ATLAS, DORA, TIBER-EU, PCI DSS, NIST SP 800-53 and ISO/IEC 27001.
Ask an AI
Ask your AI about PenTest Hub
The question is ready. Pick your assistant and it opens in a new tab with the question already written.
AI answers can be incomplete or out of date. The services and terms on this website are the ones that apply.
FAQ
Frequently asked questions
Straight answers on what we test, how we work and what to expect. Can’t find yours? Ask a senior tester and we’ll reply directly.
Where do you work?
Can you deliver DORA TLPT and TIBER-EU red teaming?
Can you test our AI systems and LLM applications?
Who will actually test our systems?
Do you use AI in your testing?
How much does a penetration test cost?
How long does a penetration test take?
When will we receive the report?
Can we see our results online?
Are retests included?
Where is our data hosted?
How is PenTest Hub related to PenTest Project?
Contact
Tell us what you need to test
A senior tester reads every message and replies directly.
What happens next
- A senior tester replieswith any questions about your scope.
- A short scoping callif your scope needs one, or straight to Flint if it is clear.
- A proposal you sign onlinewith effort, price, dates and the statement of work.
Prefer email? Write to [email protected]
